
People, roles & permissions
How roles and permissions decide who can do what, how to create a role and give it to someone, who can join your space, and what happens when someone leaves.
- For
- Administrators
- Requires
- Manage permissions
- Available on
- Web
Updated
Who can edit equipment, approve purchases, see reports or issue credentials all comes down to roles. Set them up before you invite everyone.
How roles work
A role is a named set of permissions. MakerOps comes with built-in roles, including Owner, Admin, Area Manager, Coordinator, Purchasing Agent, Staff, Student, Member and Guest. Staff is the everyday role for people who work in the space. Member, Student and Guest are for the people who use it. Out of the box Staff can look members up (read-only, so they can reach emergency contacts). Members and Students can’t browse the member directory. Student workers hold Staff and Student together, so they can.
The Owner role can do everything, whatever the matrix says. Guest comes with no permissions switched on.
You can rename any role except Admin, change what roles allow, and add your own, so your space’s list may look different.
A person can hold more than one role. They get every permission that any of their roles grants.
Some permissions are marked seat. Those only work for people who take a billable seat on your MakerOps plan. That’s your subscription, nothing to do with what you charge your own members. A person takes a seat while they hold any role other than Member, Student, Guest or Funding Source Manager, custom roles included.
The roles screen
Open Settings › Roles & Permissions. It has two tabs:
- Permissions shows the roles as columns and every permission as a row, grouped by area (Equipment, LMS, Members and so on). Click a cell to turn a permission on or off. It saves straight away.
- People shows who holds each role. Pick a role from the list to see its people. Changes save as you make them.
The screen leaves out Owner, Guest, Credit Code Admin, Billing Owner and Billing Viewer. Give those roles from the person’s page.
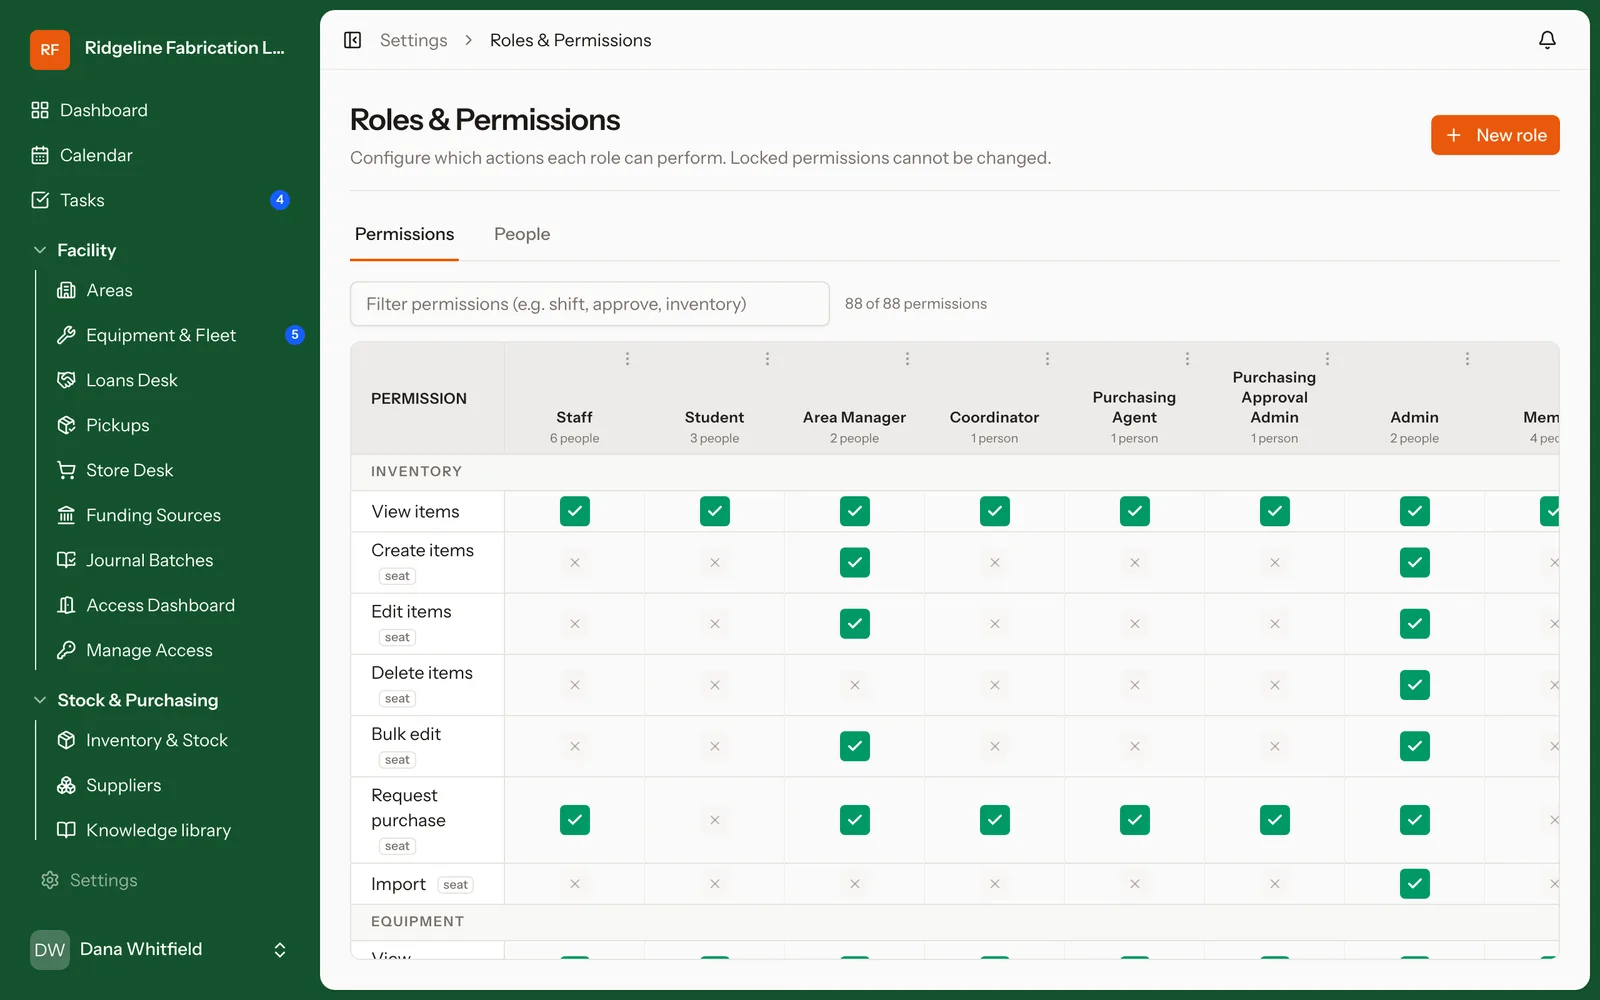
You need the Manage permissions permission to use this screen. Admins always have it: it is locked on for the Admin role.
Create a role
- In Settings › Roles & Permissions, click New role.
- Enter a Role name. Under Start from, pick an existing role to copy, or leave it as “Nothing — all off”.
- Click Create role, then tick the permissions it should have.
Each role’s column has a ⋮ menu in its header. It shows when you point at the header, and is always there on a touch screen. It has Move left, Move right, Rename… (every role except Admin) and, for a custom role, Delete…. When you delete a role, MakerOps asks which role its people should move to.
Give someone a role
Any of these works:
- From the roles screen: on the People tab, pick the role, click Add, and search for the person.
- From the person’s page: open them in People › Members & Groups. On the Overview tab, under Membership Details, tick their Roles and click Save Changes.
- Several people at once: in the Members & Groups list, select people, choose Change Role… and a role, and click Apply. This replaces each person’s roles with the one you pick.
To give one person an extra permission without changing their role, open their page and click Edit permissions. Saving a change there needs Manage permissions. Manage permissions itself can’t be given this way.
Who can give which roles
- Owners, Admins and anyone with Manage permissions can give or remove any role. Only an Owner can give or remove the Owner role.
- Anyone else who can edit members (out of the box, the Coordinator role) can only give or remove a role whose permissions they already hold themselves. They can never give Admin or Owner.
On a person’s page, a role you can’t give is greyed out, with the tip “This role has more access than your own”.
Invite people
The steps for single and bulk invitations are in Invite your people. The same rule decides which roles you can invite into:
- People with Invite members but not Edit members invite only as Member. Out of the box that is the Staff role, so student workers too.
- People with both see the staff-side roles (Staff, Admin, Area Manager and so on), Member, Student and your custom roles, minus any role with more access than their own. Only an Owner can invite an Owner.
An invitation from Invite Member carries one role. To invite student workers as Staff and Student at once, use Bulk invite, which lets you give each person several roles.
For guests, use Visiting Members (below).
Who can sign up
Choose every way people can join without an invitation on Settings › Onboarding flows. You need the Manage guest users permission.
Under Ways to sign up, each way in is a card with its rules and its QR code. The first card, Login page, is the Sign up link built into your login page, for anyone who finds it. Below it are the sign-up links you make, each with the name you gave it, for the people you hand that link or QR code to.
Everyone who signs up confirms their email address. People who wait for approval stay waiting until someone clicks Approve or Reject. Each one shows whether they have confirmed their email yet. Where they wait depends on the role they join as:
- Student or Member: People › Members & Groups, on the Approvals tab.
- Guest: People › Visiting Members, on the Pending Approval tab.
Both need the Manage guest users permission. Rejecting someone archives their account, and they can’t sign in to your space.
Make a sign-up link
A sign-up link has its own rules, so one group can join differently from another. For example, students join as Student at once, while visiting makers wait for approval. A link works even when the Sign up link on your login page is Off.
- On Settings › Onboarding flows, click New sign-up link.
- Enter a Name, such as “Students”.
- In They join as, choose Student, Member or Guest. None of them uses a plan seat. A Guest comes with no permissions switched on.
- Under What happens next, choose Instant (they can use the space once they verify their email) or Needs approval.
- Optional: under Only these email domains, click Add a domain and enter one, such as
utexas.edu. A domain also covers its subdomains, soutexas.eduacceptsmy.utexas.edu. With no domain, any address works. - Optional: choose a group in Add them to a group. People join the group once their account is active, so someone waiting for approval joins it when approved.
- Optional: choose a layout in Their dashboard (see Dashboards).
- Optional: pick a date in Stops working after. The link works through the end of that day in your space’s time zone.
- Click Create link.
The link appears with its QR code. Click Copy link, Download QR, or Print for a one-page poster. The link’s card shows how many people joined through it.
Turn On off to stop a link without deleting it; its link and QR code stop working until you turn it on again. Delete removes it for good. People who already joined through it keep their accounts.
Note: With Instant and no email domain, anyone who has the link can join right away. Add your school’s domain to keep it to your people.
The Sign up link on your login page
The Login page card is the Sign up link on your login page. It can’t be deleted; turn On off and your login page shows no Sign up link. Your sign-up links still work.
Click Edit to choose its rules:
- They join as: Member or Student.
- What happens next: Instant (anyone who verifies their email joins right away) or Needs approval (they wait for an admin).
- Only these email domains: the addresses it takes. The sign-up page tells people which ones.
Then click Save. Turning On back on opens the same window, so you choose the rules before anyone can sign up. The card’s QR code points to the sign-up page, with Copy link, Download QR and Print.
A new space starts at Needs approval. A space that signs people in with single sign-on has no Sign up link and no sign-up links.
When someone leaves
To end someone’s access, open them in People › Members & Groups and click Deactivate. To deactivate several people at once, select them in the list, choose Deactivate, and click Apply. You need the Deactivate members permission. Only an Owner can change an Owner’s status.
Warning: deactivating someone cancels their upcoming shifts and leaves them open on the schedule. Reactivate gives the person access again, but it doesn’t bring their shifts back.
To end access on a set day, set Access ends on the person’s Overview tab. They are deactivated automatically after that date.
Inactive accounts
MakerOps suspends accounts nobody has used for 180 days: no sign-in, app use, badge scan or machine session. Your admins get one email listing them. Reactivate anyone from their page. The space’s last active Owner is never suspended.
Student accounts are suspended too, unless you turn that off in Settings › Account Inactivity. To turn it off, you choose what shuts off leavers’ accounts instead.
Visitors and minors
People who only need to sign a waiver or attend an event don’t need accounts. Public links handle waivers and event sign-ups without a login (see Events, tours & the public side). Waivers support a guardian signing for a minor.
For groups who visit for a while, such as a class or a camp, use People › Visiting Members. Invite Guest has single invites, a Bulk Invite from email addresses or a CSV, and Roster + Guardians for minors. People invited there join as Member unless a CSV row gives another role.
Two-factor authentication
Everyone who signs in with a password must set up two-factor authentication. Owners and Admins reset it for someone who lost their phone, from the person’s page. See Reset someone’s two-factor for who can reset whom.
Single sign-on
SAML single sign-on is configured by MakerOps for your space, and can recognize your email domains so people land on the right sign-in. Contact us to set it up.
Once it is on, people who sign in through your organization for the first time get an account at once. Choose their role on Settings › Onboarding flows, under Single sign-on, in They join as: Guest, Student or Member. A pending invitation’s role wins over this one.
Choose the dashboard they start with in Their dashboard, next to it (see Dashboards).
Good practice
- Grant permissions through roles rather than one person at a time. It keeps audits readable.
- Keep the Admin role small. Most day-to-day staff work fits a lesser role.
- Check the matrix when you turn on a new module. Each role starts with that module’s default permissions, which may not fit how your space works.